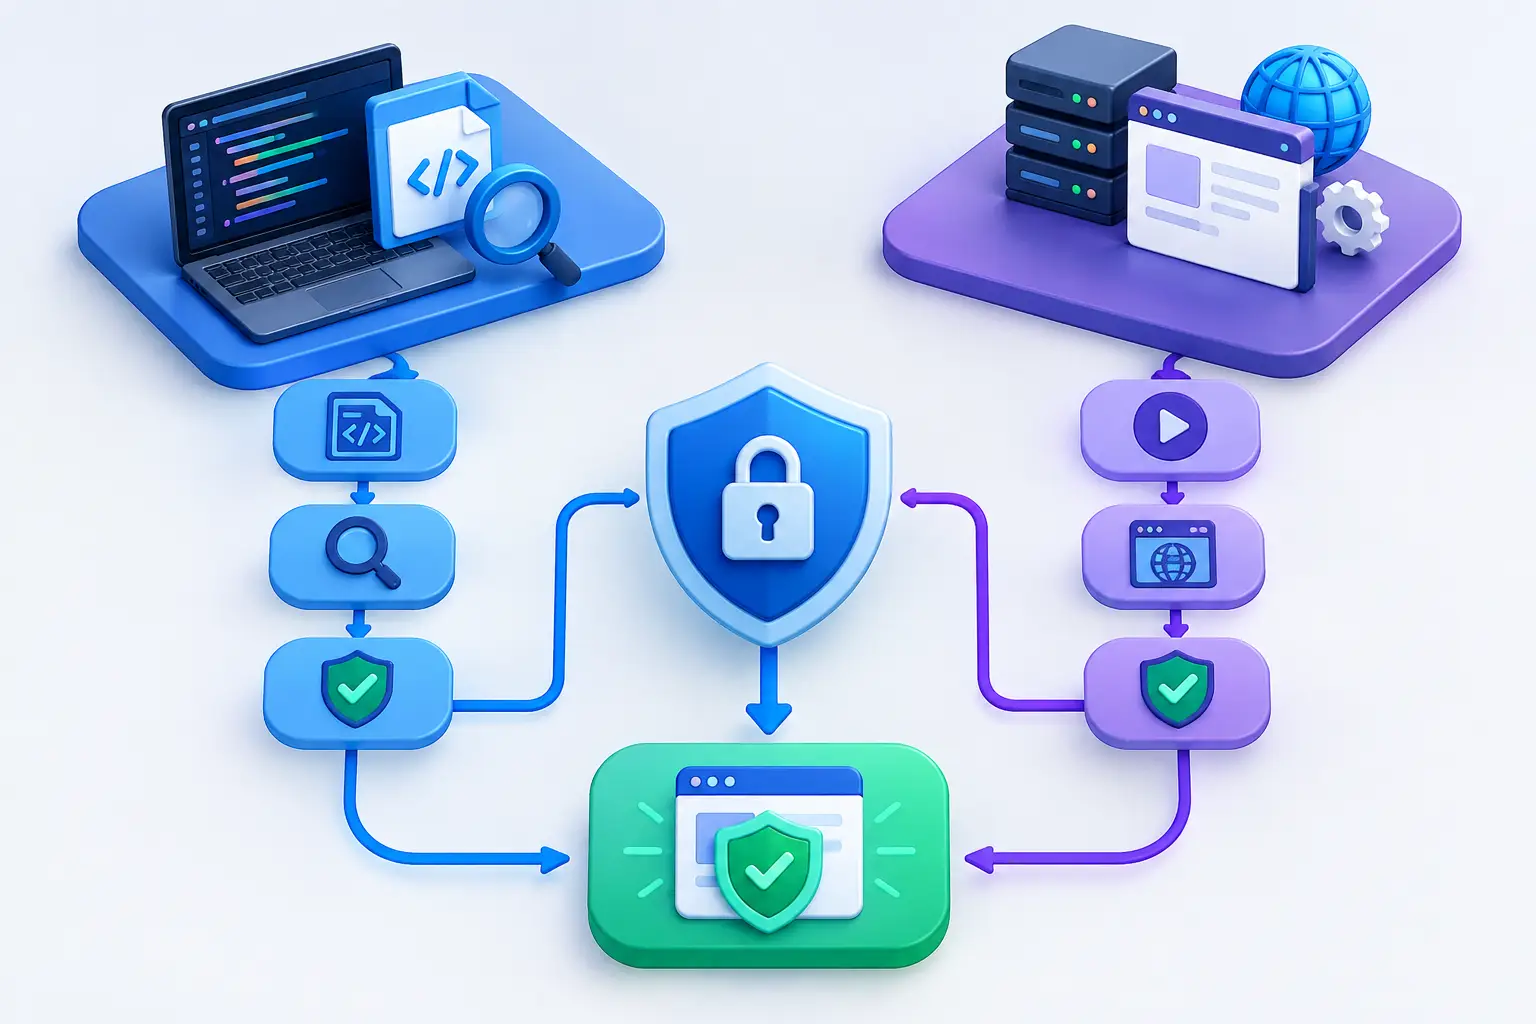
SAST versus DAST for Stronger Application Security
A web application can pass a code review and still expose sensitive records through an insecure endpoint. It can also appear secure in a production scan while carrying a weakness that becomes exploitable after a routine code change. That is why SAST versus DAST is not a choice between competing tools. It is a decision about where, when, and how your organization verifies application security.
For businesses managing customer portals, ecommerce sites, SaaS platforms, and public-facing web applications, the practical goal is clear: identify risk early, confirm what is exposed, and give technical teams a prioritized path to remediation. Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST) support different parts of that workflow.
SAST versus DAST: the core difference
SAST examines an application from the inside. It analyzes source code, bytecode, or compiled files for patterns that may introduce security flaws. Because it does not need a running application, SAST is commonly used while developers are writing code, during pull requests, or as part of a build pipeline.
DAST examines an application from the outside. It sends requests to a running website, API, or application environment and observes the response. This approach simulates how an attacker might interact with exposed functionality, looking for issues such as misconfigurations, injection weaknesses, missing security headers, and vulnerable authentication flows.
The distinction matters because each method answers a different question. SAST asks, "Could this code create a vulnerability?" DAST asks, "Can this running application be exploited or misused from the outside?"
Neither answer is complete on its own. A source code finding may not be reachable in the deployed application. A dynamic scan may miss an unsafe code path it cannot access because of authentication, complex workflow requirements, or limited test coverage.
What SAST identifies early in development
SAST is valuable because it moves security review closer to the point where software is created. Finding an unsafe database query in a pull request is usually faster and less expensive than discovering it after deployment, when the fix may require emergency changes, incident review, and customer communication.
A well-configured SAST program can identify coding patterns associated with SQL injection, cross-site scripting, insecure deserialization, weak cryptography, hardcoded credentials, and unsafe input handling. It can also help teams establish secure coding standards across multiple developers and repositories.
For organizations with active engineering teams, SAST works best when its findings are integrated into existing development practices. Developers need clear severity definitions, practical remediation guidance, and a process for reviewing false positives. A long, unprioritized list of code warnings creates alert fatigue rather than security improvement.
SAST also has limits. It may not understand how a specific deployment is configured, whether a vulnerable function is externally reachable, or how authentication and authorization behave in the live environment. It is strongest as an early-warning control, not as proof that the application is safe to expose.
Where SAST fits operationally
Use SAST when code is available and application changes are frequent. It is particularly useful for custom-built applications, internal development teams, and organizations that want security checks embedded in the software delivery lifecycle.
The most effective implementation sets expectations before deployment. Critical findings should receive review before release. High-risk findings should have an assigned owner and remediation deadline. Lower-severity findings can be tracked through a documented risk management process rather than ignored.
What DAST verifies in a live environment
DAST tests what is actually running. It sees the web server, framework behavior, exposed forms, APIs, session handling, redirects, headers, and application responses that an external user can encounter. That makes it highly relevant for businesses with public-facing assets and limited visibility into application security after release.
Dynamic testing can uncover issues that source analysis alone may not reveal, including outdated server components, missing HTTP security headers, exposed administrative interfaces, weak TLS configuration, error messages that disclose sensitive details, and vulnerabilities created by deployment settings. It is also useful when source code is unavailable, such as with third-party applications, legacy platforms, or externally managed systems.
DAST has its own trade-offs. A scan can only test pages and functions it can discover or access. If an application requires multifactor authentication, tenant-specific data, unusual user roles, or multi-step business workflows, unauthenticated scanning will see only part of the attack surface. Authenticated scanning can provide deeper coverage, but it requires careful configuration and protected test accounts.
Dynamic scans must also be managed responsibly. Aggressive testing against production systems can affect performance, trigger fraud controls, create unwanted records, or disrupt sensitive workflows. Establish a defined testing scope, scan windows, escalation contacts, and rules for handling findings before scanning begins.
DAST is not a substitute for monitoring
A DAST scan provides valuable evidence about application exposure at a point in time. It does not replace continuous oversight. New code releases, DNS changes, certificate issues, newly exposed subdomains, and changes to cloud infrastructure can alter risk between scheduled scans.
For that reason, DAST should sit within a broader security process that includes asset inventory, exposure monitoring, vulnerability tracking, remediation validation, and reporting. The scan identifies a condition. The operating model ensures the condition is understood, fixed, and checked again.
Choosing SAST, DAST, or both
The right starting point depends on your environment, but the decision should be based on coverage gaps rather than tool preference.
If your team builds and deploys custom software regularly, SAST should be introduced early. It provides developers with direct visibility into risky code patterns before those patterns reach production. If your organization operates public websites, APIs, customer portals, or third-party platforms, DAST should be part of your external security assessment process because it evaluates the environment attackers can reach.
For many small and mid-sized businesses, both are appropriate but do not need to arrive at the same time. A company with no internal software team may gain more immediate value from DAST, external exposure scanning, and ongoing domain monitoring. A growing SaaS company releasing code every week may need SAST controls first, followed by authenticated DAST against staging and production environments.
The strongest approach combines the two. SAST reduces the number of vulnerabilities introduced during development. DAST validates whether the deployed application has exploitable weaknesses or configuration failures. When both produce findings, teams can compare code-level evidence with real-world exposure and prioritize accordingly.
Build a testing workflow that leads to remediation
Security testing creates value only when findings become managed work. Whether a vulnerability comes from SAST or DAST, the response process should answer four questions: What is affected? How serious is the risk? Who owns the fix? How will remediation be verified?
Start by maintaining an accurate inventory of applications, APIs, domains, and environments. Testing cannot cover assets that have not been identified. Separate production systems from development and staging environments, and document which systems process regulated, financial, or customer data.
Next, define a consistent triage model. Severity should reflect more than a scanner score. Consider exploitability, internet exposure, affected data, business function, compensating controls, and whether a public exploit exists. A medium-severity weakness on an internet-facing customer login may deserve faster attention than a higher technical score on an isolated development system.
Assign findings to accountable owners with target dates. Development teams may own code fixes, while IT or cloud operations teams may own server, network, identity, and configuration changes. Security leadership should track overdue critical issues and accepted risks through a central reporting process.
Finally, verify closure. A ticket marked resolved is not proof that a vulnerability is gone. Rerun the relevant scan, retest the affected workflow, or review the configuration change. Document the evidence so technical leaders, auditors, and business stakeholders can see the status of risk over time.
Common mistakes that weaken application testing
The most common mistake is treating a scan report as the end of the engagement. Reports are useful, but they do not reduce risk until findings are prioritized, assigned, remediated, and validated.
Another problem is scanning only production or only pre-production. Production testing shows actual exposure, while testing earlier in the lifecycle reduces remediation cost. Coverage at both stages is more effective than relying exclusively on either one.
Organizations also underestimate authentication and asset discovery. A DAST scan that cannot log in may miss the highest-value areas of an application. A SAST deployment that excludes older repositories may leave critical business functions outside the program. Scope should be reviewed whenever applications, domains, teams, or vendors change.
FortifyNET supports this operational discipline by connecting security analysis with actionable remediation planning, documented reporting, and continuous visibility across web and network environments.
Make application security measurable
Security leaders need more than a count of open findings. Track time to remediate critical and high-severity vulnerabilities, the number of recurring findings, coverage of known applications, overdue remediation items, and the rate at which new releases introduce security issues. These measures show whether the program is improving or merely generating alerts.
SAST and DAST are most effective when they support a repeatable cycle: identify weaknesses, understand business impact, remediate with clear ownership, and verify the result. The useful question is not which tool wins. It is whether your organization can see the risks in its software before attackers do, and act on them with discipline.