How to Build a Vulnerability Remediation Plan
A vulnerability scan that produces 300 findings is not a plan. It is a backlog, and without a clear response model, that backlog turns into accepted risk by default. A vulnerability remediation plan gives your organization a disciplined way to decide what gets fixed first, who owns each action, how progress is tracked, and where ongoing monitoring fits into daily operations.
For small and mid-sized businesses, this matters because most teams do not have excess time or specialized security staff. They have websites to keep online, email systems to protect, vendors to manage, and compliance questions to answer. A workable plan translates technical findings into business action so remediation can happen consistently instead of only after a serious alert.
What a vulnerability remediation plan actually does
A vulnerability remediation plan is the operating framework that connects discovery to resolution. It should not stop at identifying weaknesses. It should define how vulnerabilities are validated, prioritized, assigned, remediated, tested, documented, and monitored over time.
That distinction is important. Many organizations run scans regularly but still struggle with exposure because results are scattered across spreadsheets, ticket queues, and email threads. Security data exists, but there is no controlled path from finding to closure. The result is predictable - duplicate effort, unresolved high-risk items, and limited visibility for leadership.
A useful plan creates control in four areas. It establishes risk-based priorities, assigns accountability, sets remediation expectations, and preserves evidence of action. Those four elements support both day-to-day security operations and broader governance requirements.
Start with business context, not just severity scores
One of the most common mistakes in a vulnerability remediation plan is treating scanner severity as the only decision factor. Severity matters, but it is not enough on its own. A medium-severity issue on a public-facing login page may deserve faster action than a high-severity issue on an isolated internal system with compensating controls.
Your plan should consider where the asset sits, what data it handles, how exposed it is, and whether the vulnerability is exploitable in a realistic attack path. This is where security operations become practical rather than theoretical. A public web application, externally reachable management interface, or email-related weakness often carries more immediate business risk than a technical score alone suggests.
For that reason, remediation planning should begin with asset inventory and classification. If you do not know which systems are public-facing, business-critical, regulated, or vendor-managed, prioritization will be inconsistent. Teams need enough asset context to answer basic questions quickly. What does this system do? Who owns it? Is it internet-exposed? Does it process customer or financial data? Is there an existing compensating control?
Build the plan around a clear remediation workflow
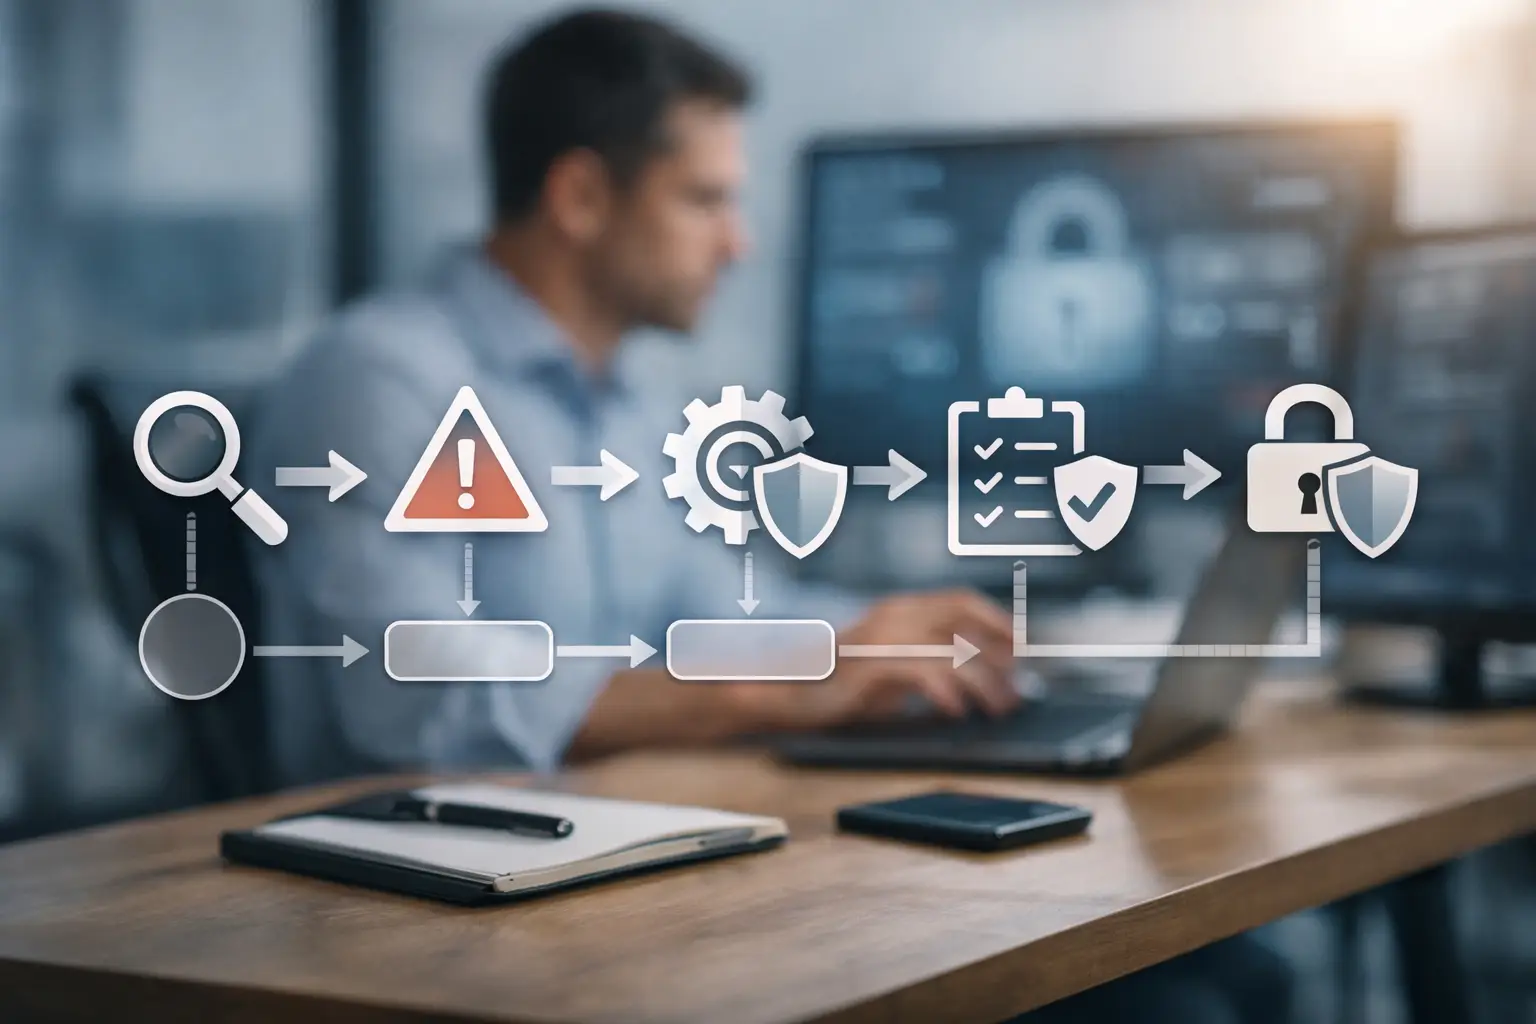
A strong vulnerability remediation plan follows a repeatable workflow. The exact sequence may vary by organization, but the structure should be stable enough that teams know what happens after a finding appears.
The first step is validation. Not every finding should move straight into active remediation. Some results are duplicates, false positives, or already mitigated through configuration or architecture. Validation protects your team from wasting effort and keeps reporting credible.
The second step is prioritization. This is where business impact, exploitability, exposure, and compliance relevance come together. It helps to define internal remediation tiers such as critical, high, medium, and low, but those tiers need clear rules behind them. If every item becomes urgent, nothing is.
The third step is assignment. Every finding needs an owner, and that owner should be specific. Not “IT” or “security team,” but the application lead, infrastructure administrator, hosting provider, or vendor contact responsible for the fix. Ownership is what moves issues out of reports and into operational queues.
The fourth step is remediation execution. Depending on the issue, that may involve patching, configuration changes, code fixes, access control changes, service hardening, certificate updates, or disabling unnecessary exposure. In some cases, full remediation is not immediately possible. Your plan should allow for interim mitigation when risk must be reduced before a permanent fix can be deployed.
The fifth step is verification. If a vulnerability was marked fixed, there should be evidence that it is no longer present. That usually means rescanning, retesting, or validating the changed state in a controlled report. Closing issues without verification creates a false sense of progress.
Set remediation timelines that reflect real risk
Remediation deadlines should be realistic, but they also need to create urgency where it matters. Many organizations define service-level targets for vulnerability classes. For example, a critical internet-facing issue may require action in days, while a low-risk internal finding may be scheduled into a normal maintenance window.
That said, fixed timelines alone can create blind spots. A known exploited vulnerability on a public-facing asset should move faster than a generic critical issue with limited exposure. On the other hand, an old unsupported system may require a controlled exception process instead of repeated overdue notices that no one can realistically resolve.
This is why exception handling belongs inside the plan, not outside it. If a vulnerability cannot be remediated on time, the organization should document the reason, the temporary safeguards in place, the business owner accepting the risk, and the date for review. That keeps delayed remediation visible and governed instead of informally ignored.
Reporting should support action, not just documentation
A remediation plan fails when reporting serves only auditors or monthly reviews. The report needs to help operational teams decide what to do next. That means findings should be organized by priority, affected asset, owner, status, and due date, with enough technical detail to support remediation without overwhelming non-technical stakeholders.
Leadership visibility matters as well. Business owners and operations leaders do not need every port, version string, or scanner output. They need to know where material risk exists, whether critical items are trending down, which systems remain exposed, and whether remediation performance is improving.
A centralized dashboard helps here because it reduces fragmentation. Instead of forcing teams to reconcile separate exports from web scans, network scans, domain monitoring, and email oversight, a single reporting view creates continuity. That continuity is what allows a vulnerability remediation plan to function as an ongoing management process rather than a periodic project.
Continuous monitoring changes the quality of the plan
The best remediation plans are not written once and left alone. They improve as new assets appear, old systems change, and threat activity shifts. Continuous monitoring is what keeps the plan current.
This is especially important for businesses with growing public-facing environments. A newly exposed subdomain, a misconfigured mail record, an expired certificate, or a vulnerable web component can introduce risk between scheduled assessments. If visibility is limited to occasional scans, remediation starts late and often under pressure.
Continuous monitoring allows teams to identify new findings earlier, verify whether fixes hold over time, and maintain a defensible record of security oversight. It also supports more accurate prioritization because teams are working from current exposure data rather than stale reports.
For many organizations, this is where outside support becomes valuable. A consultative and platform-backed process can help translate findings into tracked actions, provide structured reporting, and maintain oversight when internal teams are stretched. FortifyNET approaches remediation this way - as an ongoing discipline supported by visibility, defined workflows, and administrative control.
Common breakdowns to avoid
Most remediation challenges are operational, not theoretical. The first breakdown is unclear ownership. If no one knows who is responsible for a finding, the issue remains open until it becomes urgent. The second is poor asset context, which causes teams to misjudge exposure and business impact.
The third is overreliance on scanner scores. Severity is useful, but remediation decisions need context. The fourth is weak verification. Teams may apply a patch or configuration change without confirming the vulnerability is actually gone. The fifth is treating exceptions as permanent. Temporary acceptance needs review, or it becomes silent normalization of risk.
A mature vulnerability remediation plan does not eliminate every vulnerability immediately. That is not realistic for most businesses. What it does is create a controlled method for reducing exposure, documenting decisions, and keeping leadership aware of where risk stands.
Make the plan usable across teams
Security does not remediate everything on its own. Infrastructure teams patch servers. Developers fix application flaws. Email and domain administrators update configurations. Vendors may own parts of the environment your business still depends on. Your plan should reflect that shared reality.
Use language that each group can act on. Define what information must be included in a remediation ticket, what evidence is needed for closure, when issues should be escalated, and how exceptions are approved. If the process is too technical for business owners or too vague for administrators, it will break in practice.
The strongest plans are the ones teams will actually use under normal operating conditions, not just during audits or incident response. If your current process produces more findings than decisions, the next improvement is not another scan. It is a clearer, more disciplined path from visibility to action.